Create your first S3 bucket
This guide walks you through creating your first S3 bucket from the Hikube console, up to uploading your first file.
Objectives
By the end of this guide, you will have:
- An operational S3 bucket in your project
- An S3 user with their access key pair
- A first file uploaded with
awsormc
Prerequisites
- A Hikube account and a project (see the Hikube quick start)
- An S3 client installed on your workstation: AWS CLI or MinIO Client (
mc)
Step 1: Open the creation wizard
- Log in to the Hikube console and select your project.
- In the side menu, open Infrastructure → S3 Buckets. The Object Storage Buckets page is displayed.
- Click Create a bucket.
Step 2: Configure and create the bucket
The wizard has three steps.
General
- Enter the Bucket name (a name is suggested by default). Rules: lowercase letters, digits and hyphens; starts with a letter and ends with a letter or a digit; 16 characters maximum. Example:
demo-assets. - For this guide, leave these options unchecked:
- Enable Object Lock (WORM): each object is locked for 365 days after it is written, in COMPLIANCE mode; no one can modify or delete it before then. The duration cannot be changed, locking cannot be removed after creation, and deleting the bucket does not delete its objects;
- Enable encryption at rest (LUKS): encrypts the stored data; cannot be changed after creation.
- Click Next.
Users
- Enter the Username (for example
app-user): 3 to 16 characters, same rules as the bucket name. - Leave Read only set to No to get read and write access.
- Click Add, then Next.
At least one user is required to continue.
Summary
The Summary displays the name, the project, the number of users to create, the locking status (Enabled (365 days, COMPLIANCE) when checked) and the encryption status, and the Estimated Cost per GB. Click Create bucket.
During creation, the button displays Creating... then Provisioning bucket…: the console waits for the bucket to be ready before creating the users.
Step 3: Check the bucket status
The final screen displays Bucket successfully created. After retrieving the credentials (step 4), click Finish: the console opens the bucket page.
On this page:
- the status badge shows Ready when the bucket is operational (Provisioning while it is being provisioned, Error if the platform could not create it: see troubleshooting);
- the WORM and LUKS badges show the locking and encryption status;
- the Access & Configuration card displays the S3 Bucket name and the Endpoint;
- the Users & Access card lists the users and their permission (Read-only or Read / Write).
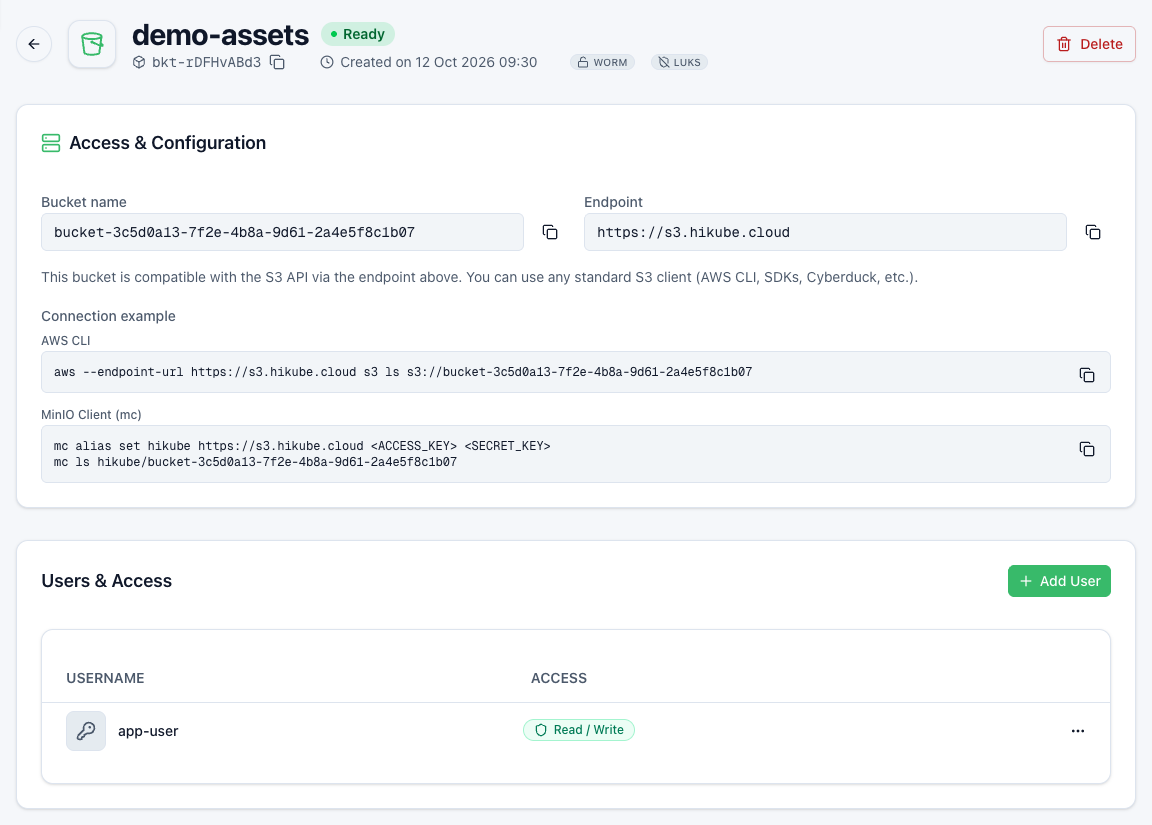
If the bucket is not ready in time, the console displays "Bucket provisioning" and does not create the users. Wait until the bucket switches to Ready, then create them from its page with Add User (see Manage users and access keys).
Step 4: Retrieve the credentials
The final screen of the wizard displays, for each user created:
| Field | Usage |
|---|---|
| S3 Bucket Name | Actual bucket name to use in your commands and SDKs |
| Access Key | Access Key ID |
| Secret Key | Secret Access Key |
| API Endpoint (S3) | S3 endpoint, for example prod.s3.hikube.cloud |
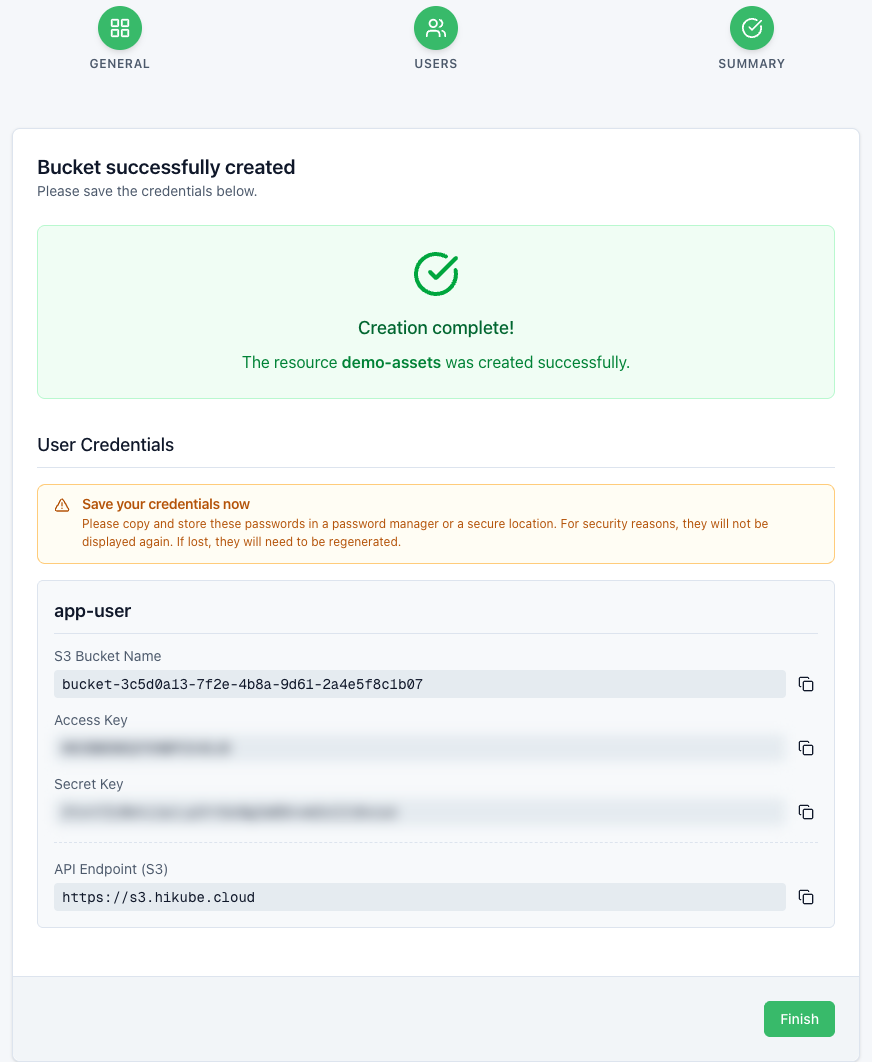
Copy these values before clicking Finish and store the secret key in a password manager. It will not be displayed again. If it is lost, create a new user.
The S3 Bucket Name is generated by the platform, as bucket- followed by a unique identifier (for example bucket-1df67984-321d-492d-bb06-2f4527bb0f5b). It differs from the name entered in the wizard: an S3 client configured with the latter receives AccessDenied. Always use the S3 name in your clients. It remains available on the bucket page.
If it is not known yet, the screen displays "The S3 name will be available in a few moments, on the bucket page." in its place: get it from the Access & Configuration card of the bucket page. The endpoint, too, only appears once it is known.
Export the values in your terminal:
export S3_ENDPOINT="https://<endpoint>"
export AWS_ACCESS_KEY_ID="<clé-d-accès>"
export AWS_SECRET_ACCESS_KEY="<clé-secrète>"
export BUCKET_NAME="<s3-bucket-name>"
If the endpoint is displayed without a prefix (for example prod.s3.hikube.cloud), add https:// in front of it: the aws and mc clients expect a full URL.
Step 5: Connect and test
A user's keys do not grant permission to list all the buckets of the endpoint. Commands must always target your bucket: s3://$BUCKET_NAME/ or hikube/$BUCKET_NAME/.
Option A: AWS CLI
# Upload a test file
echo "hello hikube" > /tmp/hello.txt
aws --endpoint-url "$S3_ENDPOINT" s3 cp /tmp/hello.txt "s3://$BUCKET_NAME/hello.txt"

# List the bucket contents
aws --endpoint-url "$S3_ENDPOINT" s3 ls "s3://$BUCKET_NAME/"
Option B: MinIO Client (mc)
# Define an alias for the endpoint
mc alias set hikube "$S3_ENDPOINT" "$AWS_ACCESS_KEY_ID" "$AWS_SECRET_ACCESS_KEY"

# Upload a test file, then list the bucket
mc cp /tmp/hello.txt "hikube/$BUCKET_NAME/hello.txt"
mc ls "hikube/$BUCKET_NAME/"
Expected result: the hello.txt file appears in the list.
The Access & Configuration card on the bucket page provides these commands, already filled in with the endpoint and the bucket name, in the Connection example section.
Step 6: Quick troubleshooting
| Symptom | Probable cause | Action |
|---|---|---|
AccessDenied on aws s3 ls without a bucket | Listing the whole endpoint | Target s3://$BUCKET_NAME/ |
AccessDenied although the command targets the bucket | Name entered in the wizard used instead of the S3 name | Use the Bucket name (bucket-…) displayed in Access & Configuration |
AccessDenied on write | User set to Read-only | Change their permission with Edit access |
SignatureDoesNotMatch / InvalidAccessKeyId | Incorrect or incomplete keys | Copy the keys again; if the secret key is lost, create a new user |
| Connection error | Endpoint without https:// | Prefix the endpoint with https:// |
See also the full troubleshooting guide.
Step 7: Cleanup
- Delete the test file:
aws --endpoint-url "$S3_ENDPOINT" s3 rm "s3://$BUCKET_NAME/hello.txt"
- On the bucket page, click Delete (or, from the list, open the bucket's actions menu and choose Delete).
- Enter the exact bucket name in Resource name to confirm, then click Permanently delete.
Deleting a bucket is permanent and removes all its objects, even if it is not empty. Copy the data you want to keep before deleting it. A locked bucket (WORM) is the exception: it is removed from the console, but its objects are kept and stay locked for 365 days after they were written.